
Preserving Legacy Real-Time Applications Through Virtualization
Real-time applications often remain in service much longer than the hardware on which they were originally developed. Test systems, industrial controls, simulation environments, and data-acquisition platforms may operate for decades because replacing the application would be expensive, disruptive, or technically risky.
Over time, maintaining the original environment becomes increasingly difficult. Processors and motherboards are discontinued. Storage devices fail. Replacement interface cards become scarce. Older operating systems may not support current hardware, while newer operating systems may not support the application or its drivers.
Virtualization can help separate the lifecycle of the software from the lifecycle of the physical computer. An established operating environment can be placed in a virtual machine and run on newer hardware without rebuilding the complete application stack.
This approach can extend the useful life of a system, but it is not an automatic solution. Timing behavior, hardware access, software licensing, security, and validation still need to be examined carefully.
Why Legacy Real-Time Applications Are Difficult to Replace
A legacy application is not necessarily poorly designed or obsolete. In many cases, it continues to perform its intended function reliably.
The difficulty is that the application usually depends on more than its own source code. Its operating environment may include:
- A particular operating-system release
- Specific kernel behavior
- Older runtime libraries
- A particular compiler and build process
- Custom kernel modules or device drivers
- Specialized PCI or PCIe hardware
- Fixed CPU, interrupt, and memory assignments
- Licensing tied to physical hardware
- Supporting scripts, tools, and configuration files
- Interfaces to other established systems
Changing one component can affect the others. Upgrading the operating system may require a new driver. The new driver may behave differently under load. Rebuilding the application with a current compiler may change execution behavior. Moving to a new interface card may alter the timing of the I/O path.
For a timing-sensitive application, functional compatibility is only part of the problem. The modernized system must also continue to meet its response-time and consistency requirements.
The Aging-Hardware Problem
Organizations sometimes preserve a legacy application by purchasing spare computers or replacement components before the original platform disappears from the market.
This can extend the system’s life, but it becomes less practical over time.
Real-time virtualization differs from conventional server virtualization in an important respect: resource allocation cannot be based only on average utilization.
A replacement component may have been stored for years without being tested. Firmware versions can differ. Drives and power supplies deteriorate even when unused. Technicians familiar with the original hardware may retire or move to other roles. Eventually, the organization may rely on a small collection of parts with no dependable replacement source.
Older hardware can also become more expensive to maintain than newer equipment. A system may require:
- Specialized repair services
- Used or refurbished components
- Additional spare computers
- Obsolete storage or network interfaces
- More rack space, power, and cooling
- Manual configuration processes
- Exceptions to current IT and security practices
At some point, preserving the physical platform can present more risk than moving the application.
How Virtualization Changes the Lifecycle
Virtualization places an abstraction layer between the operating environment and the physical computer.
The virtual machine can retain its existing operating system, application, libraries, and configuration while the host runs on a newer hardware platform. From the application’s perspective, much of the software environment remains familiar even though the physical system has changed.
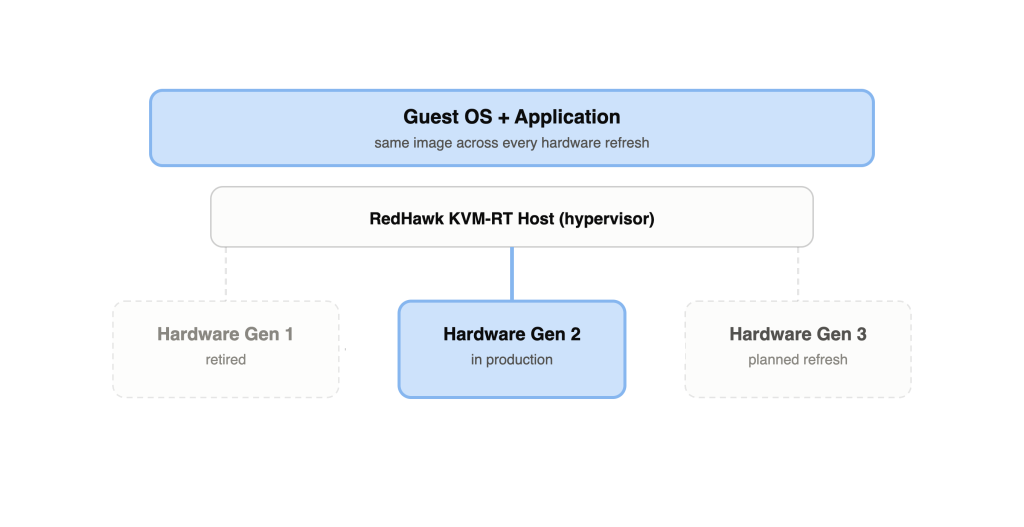
This separation can provide several benefits:
- The application is less dependent on one generation of server hardware.
- Virtual-machine configurations can be reproduced more consistently.
- Older and newer operating environments can run on the same host.
- Multiple legacy computers may be consolidated.
- System images can be backed up and restored more easily.
- Hardware replacement may require fewer changes to the application.
- Development and test copies of the environment can be created without another original computer.
The main value is controlled change. Rather than replacing the hardware, operating system, drivers, application, and interfaces at the same time, the engineering team can preserve parts of the existing environment while addressing others separately.
Virtualization Does Not Preserve Everything Automatically
A virtual-machine image can capture disks, operating-system files, applications, and configuration data. It does not automatically reproduce every characteristic of the original physical system.
The new environment may have:
- A different processor architecture or topology
- More processor cores
- Different cache behavior
- A NUMA memory layout
- Different timers
- New network and storage devices
- A hypervisor between the guest and hardware
- Different interrupt routing
- Different firmware and power-management behavior
An application that depends only on standard operating-system services may transition relatively easily. An application with strict timing requirements or direct hardware dependencies requires more investigation.
Virtualization should therefore be treated as an engineering migration, not simply as copying an old disk into a virtual machine.
Start by Documenting the Existing System
Before deciding how to preserve an application, teams need to understand what the application actually depends on.
Legacy systems are often poorly documented because their configuration evolved gradually. The original engineers may no longer be available, and operating knowledge may exist mainly in handwritten notes or individual experience.
A useful system inventory should include:
- Computer and processor models
- Installed memory
- Storage devices and filesystems
- Operating-system and kernel versions
- Boot parameters
- Application versions
- Libraries and runtime dependencies
- Drivers and kernel modules
- PCI and PCIe devices
- Network interfaces and addresses
- CPU assignments
- Interrupt assignments
- Timing and synchronization sources
- External equipment and communication protocols
- License files, keys, or hardware dongles
- Startup and shutdown procedures
- Development tools and source-code availability
- Known performance and timing requirements
The team should also record how the system is tested. Without a baseline, it will be difficult to determine whether the virtualized version preserves the necessary behavior.
Determine What Must Remain Unchanged
Not every part of the original system needs to be preserved.
The application might require its original operating system and libraries but work with a newer network adapter. Another application may tolerate a newer compiler but depend on a specialized I/O card. A third may need to preserve the complete guest software environment while changing how data is stored.
Classifying the dependencies helps define the migration.
| Component | Possible approach |
| Application binaries | Preserve within the guest |
| Operating system | Preserve or update separately |
| Runtime libraries | Preserve with the application |
| Standard networking | Replace with a virtual network device |
| General storage | Move to virtualized storage |
| Specialized I/O | Pass through a compatible physical device |
| Obsolete interface card | Replace, emulate, or redesign the interface |
| Hardware-bound license | Rehost or obtain a revised license |
| Development environment | Archive or reproduce in a separate VM |
This evaluation can also reveal that parts of the application should be updated before virtualization. Preserving an environment does not require preserving every weakness indefinitely.
Timing Requirements Need a Baseline
These requirements should be measured on the existing system when possible. Historical requirements documents can help, but the actual system may differ from its original specification after years of modifications.
Testing should include representative operating conditions. An application may appear stable when the system is idle but behave differently during heavy I/O, logging, network traffic, or concurrent processing.
The baseline provides a point of comparison for the virtualized system. Without it, the team may know that the new system behaves differently but not whether that difference matters.
CPU and Memory Configuration
The original application may have been designed for a computer with one processor socket and a small number of cores. A current server may contain multiple sockets, NUMA nodes, shared caches, and simultaneous multithreading.
Giving the virtual machine the same number of processors as the original system does not necessarily reproduce its behavior.
CPU pinning, CPU shielding, NUMA-aware memory placement, and interrupt affinity can help create a controlled environment for the guest.
See How CPU Shielding, NUMA, and Interrupt Affinity Affect Real-Time Virtual Machines for how to map physical cores, memory, and interrupts to a real-time guest.
The objective is not to make the new server physically identical to the original. It is to give the application a resource configuration that meets its measured requirements consistently.
Specialized Hardware Can Be the Deciding Factor
Hardware compatibility is often the largest obstacle to virtualizing a legacy real-time application.
The original system may use a custom or discontinued device for:
- Data acquisition
- Analog or digital I/O
- Motion control
- Timing and synchronization
- CAN or serial communication
- FPGA processing
- MIL-STD-1553 communication
- Sensor interfaces
- Proprietary bus communication
Several approaches may be possible.
Pass Through the Existing Device
If the device uses a compatible PCIe interface and the guest driver continues to work, PCI passthrough may allow the virtual machine to control it directly.
This approach should be tested for IOMMU compatibility, interrupt behavior, device reset behavior, and NUMA locality. Older PCI devices may also require adapter hardware or may not be supported in a current server.
Replace the Device
A newer device may provide equivalent functions, but it may require a new driver or application changes. The replacement should be evaluated as a separate technical change rather than assumed to be transparent.
Move the Interface Outside the Host
In some cases, an external Ethernet-based or network-connected I/O system can replace a device installed inside the original computer. This can reduce dependence on a particular host architecture, although it changes the I/O path and must be tested for timing suitability.
Emulate the Device
Device emulation may be possible when the interface is well understood and the application’s timing requirements permit it. Custom emulation can become a substantial development and maintenance project, especially when the original hardware behavior is not fully documented.
Retain a Hybrid Architecture
The legacy application can run in a virtual machine while a separate physical system manages the specialized hardware. The two systems then exchange data through a controlled interface.
This preserves more of the software environment without requiring every hardware dependency to operate inside the guest.
Licensing Can Block an Otherwise Practical Migration
Older software licenses may be tied to:
- A processor or motherboard identifier
- A network-interface address
- A physical USB or parallel-port dongle
- A disk serial number
- A particular hostname
- A license server
- A discontinued activation service
A virtual machine will not necessarily present the same identifiers as the original hardware. Even if a virtual platform can reproduce an identifier, doing so may not comply with the license agreement.
Licensing should be investigated early. The software vendor may be able to rehost the license, provide a virtual-machine-compatible license, or issue a replacement for obsolete licensing hardware.
If the vendor no longer exists, the organization may need legal and technical review before selecting a migration approach. Discovering an unresolvable licensing issue after the technical work is complete can delay or prevent deployment.
Security and Unsupported Operating Systems
Virtualization can isolate an older operating system from some external activity, but it does not make the operating system secure.
An unsupported guest may contain known vulnerabilities that will never receive patches. It may also require older network protocols, weak authentication methods, or outdated administrative tools.
Potential controls include:
- Placing the guest on a restricted network
- Limiting connections to required systems
- Disabling unnecessary services
- Using host-level firewalls
- Separating administrative and application traffic
- Restricting internet access
- Monitoring communication into and out of the guest
- Controlling access to virtual-machine images
- Documenting accepted risks and compensating controls
Snapshots and backups can help restore a damaged environment, but restoration is not a substitute for preventing unauthorized access.
Security teams should be involved before the system is deployed, particularly when the virtualized application will connect to production networks or physical equipment.
Validation and Qualification
Moving an established application to a virtual machine changes the execution environment, even when the guest operating system and application files remain unchanged.
The amount of validation required depends on the application and industry. A laboratory tool may require internal acceptance testing, while an aerospace, medical, industrial, or defense system may be subject to formal qualification and configuration-control processes.
A migration plan should define:
- Which components are changing
- Which requirements must be retested
- How timing behavior will be measured
- Which external interfaces will be exercised
- What representative loads will be applied
- How results will be compared with the original system
- Who can approve the new configuration
- Which hardware and software versions become part of the controlled baseline
The virtualized system should be tested under realistic load, including activity from other virtual machines and host services that will exist in production.
Testing only the guest in isolation may miss resource conflicts introduced later.
Virtual-Machine Images Improve Recovery, but Require Discipline
One benefit of virtualization is the ability to capture an operating environment as a set of managed files. Those files can be backed up, copied, and restored without rebuilding the system manually.
This can improve recovery from hardware failure, but only if the organization manages the images carefully.
Teams should control:
- The approved production image
- Image versions and changes
- Host and hypervisor compatibility
- Configuration files stored outside the image
- Passed-through device assignments
- License files and activation requirements
- Backup frequency and retention
- Access to sensitive application data
- Procedures for verifying a restored system
A snapshot is not always a complete backup. Snapshots may depend on the original virtual disk and can grow or degrade performance if retained indefinitely.
Recovery procedures should be tested on an independent system. An untested backup provides limited assurance.
Consolidation Should Be Deliberate
Virtualization may allow several legacy computers to be consolidated on one current server. This can reduce rack space, cabling, power use, and the number of physical systems that must be maintained.
It can also create a shared point of failure.
Before consolidating multiple applications, engineers should evaluate:
- Whether the workloads can share a host safely
- Which resources must be isolated
- Whether applications need direct access to separate devices
- What happens if the host fails
- Whether maintenance can interrupt all applications simultaneously
- Whether a standby host is required
- How virtual machines will be restored or moved
- Whether the combined workloads have been tested together
Systems should not be consolidated merely because sufficient average CPU and memory capacity appears available. Real-time applications need to be evaluated according to their peak activity and response requirements.
When Virtualization Is a Strong Sustainment Option
Virtualization is particularly useful when:
- The application remains valuable and stable.
- The original hardware is difficult to maintain.
- The operating system does not support current server hardware.
- The application relies mainly on standard processor, memory, network, and storage services.
- Required PCIe devices can be passed through or replaced.
- Multiple operating-system versions must coexist.
- Rebuilding the application would require substantial development or requalification.
- The virtualized environment can be tested against a documented baseline.
- Security and licensing requirements can be addressed.
In these situations, virtualization can reduce the number of changes required at one time and provide a more manageable hardware foundation.
When Virtualization May Not Be the Right Answer
Virtualization may be unsuitable when:
- The application’s timing requirements cannot be met consistently.
- Essential hardware cannot be passed through, replaced, or emulated.
- The application depends on undocumented characteristics of the original machine.
- Required licenses cannot be transferred.
- The guest operating system creates unacceptable security risk.
- The new architecture would require more custom work than updating the application.
- The original system cannot be tested well enough to establish a baseline.
- Formal qualification rules make preservation impractical.
In these cases, porting, rewriting, or replacing the application may provide a better long-term outcome.
A hybrid approach may also be appropriate. Some functions can remain on dedicated physical hardware while other parts of the environment are virtualized.
A Practical Migration Process
1. Inventory the Existing Environment
Document the hardware, operating system, applications, libraries, drivers, devices, licenses, network connections, and operating procedures.
2. Establish Functional and Timing Baselines
Measure the original system under representative conditions. Record both expected behavior and known limitations.
3. Classify the Dependencies
Separate dependencies that must remain unchanged from those that can be updated, replaced, or removed.
4. Evaluate Hardware Interfaces
Determine whether each device can be passed through, replaced, moved outside the host, emulated, or handled by another system.
5. Review Licensing and Security
Confirm that the software can legally and technically run in a virtual machine. Define controls for unsupported operating systems.
6. Build a Proof of Concept
Create the virtual machine and verify basic application operation before finalizing the production hardware and architecture.
7. Configure Physical Resources
Assign processors, memory, interrupts, and I/O devices deliberately. Reserve sufficient resources for the host.
8. Test Under Representative Load
Exercise the application, host, other virtual machines, network, storage, and physical interfaces together.
9. Compare Results With the Baseline
Evaluate both functional output and timing behavior. Investigate differences rather than assuming that a faster processor makes them irrelevant.
10. Document and Control the New Environment
Record the approved virtual-machine image, host configuration, firmware, device placement, licenses, and recovery procedures.
11. Plan for the Next Migration
Virtualization reduces dependence on the current host, but it does not eliminate future change. Preserve the documentation, installation files, source code, build tools, and test procedures needed for the next hardware transition.
Preservation Is Not the Same as Avoiding Change
Virtualization can preserve a legacy operating environment while moving it away from aging physical hardware. It can reduce the number of components that need to change at once and provide a more reproducible foundation for continued operation.
The process still requires careful engineering. Timing requirements must be measured. Hardware interfaces need a workable migration path. Licensing and security issues must be resolved. The completed system must be validated under realistic conditions.
RedHawk KVM-RT can support virtualized configurations in which processor, memory, interrupt, and I/O resources are deliberately assigned to timing-sensitive guests. Whether virtualization is the appropriate sustainment strategy still depends on the application, its hardware dependencies, and its lifecycle requirements.
The objective should not be to preserve every component indefinitely. It should be to retain the application’s required behavior while replacing the parts of the system that have become difficult or risky to maintain.
Frequently Asked Questions
Can an existing real-time application be moved into a virtual machine without modifying it?
Sometimes. Applications that rely on standard operating-system services may require few changes. Applications that use specialized devices, hardware-bound licenses, or undocumented timing assumptions may require driver, configuration, or application updates.
Does virtualization reproduce the timing of the original computer?
Not automatically. The new host has different processors, memory, interrupts, devices, and scheduling behavior. The virtualized system must be configured and tested against the application’s actual timing requirements.
Can a virtual machine preserve an unsupported operating system safely?
Virtualization can help isolate the system, but it does not remove vulnerabilities within the guest. Network restrictions, access controls, monitoring, and other compensating measures may be required.
What happens if a legacy application needs a discontinued PCI card?
Possible options include passing through the existing card, finding a supported replacement, moving the interface to an external system, emulating the device, or retaining a hybrid physical and virtual architecture. Compatibility must be evaluated for the specific device.
Is virtualization better than rewriting a legacy application?
It depends on the system. Virtualization may be preferable when the application remains reliable and rebuilding it would create substantial cost or qualification risk. Rewriting may be more appropriate when hardware, security, licensing, or maintainability problems cannot be resolved within a virtual environment.
Related Articles
-

Native Real-Time Linux vs. Real-Time Virtualization: Which Architecture Fits Your Application?
Native Real-Time Linux vs. Real-Time Virtualization: Which Architecture Fits Your Application? Virtualization is now common in enterprise computing, but timing-sensitive systems introduce requirements that conventional IT workloads do not share. An application may…
-

How CPU Shielding, NUMA, and Interrupt Affinity Affect Real-Time Virtual Machines
How CPU Shielding, NUMA, and Interrupt Affinity Affect Real-Time Virtual Machines Running a real-time operating system inside a virtual machine does not automatically create a deterministic environment. The virtual machine still depends…
-

Choosing an I/O Strategy for Real-Time Virtual Machines
Choosing an I/O Strategy for Real-Time Virtual Machines Processor allocation receives considerable attention when engineers design a real-time virtualized system. However, an application that interacts with physical equipment also depends on the…