
Native Real-Time Linux vs. Real-Time Virtualization: Which Architecture Fits Your Application?
Virtualization is now common in enterprise computing, but timing-sensitive systems introduce requirements that conventional IT workloads do not share. An application may need to respond within a defined time window, maintain consistent behavior under load, or interact with physical equipment through specialized I/O.
For these systems, the question is not simply whether an application can run in a virtual machine. The more important question is whether virtualization supports the application’s timing, isolation, hardware-access, and lifecycle requirements.
Native real-time Linux and real-time virtualization can both support demanding applications, but they solve different problems. The right choice depends on what the system must do and which tradeoffs the engineering team can accept.
What Is a Native Real-Time Linux System?
In a native deployment, the real-time operating system runs directly on the physical hardware. Applications, drivers, system services, and development tools operate within that environment without a hypervisor between the operating system and the processor.
This direct relationship with the hardware gives engineers greater control over processor assignment, memory placement, interrupt handling, scheduling, and I/O. It also removes a layer of software that could affect timing behavior.
Native deployment is often the most appropriate architecture when the primary objective is achieving the lowest practical latency and jitter. It can also simplify systems that contain a single critical workload and do not need to support multiple operating environments.
However, a native architecture may require separate physical systems when applications depend on different operating systems, incompatible software versions, or conflicting configurations. As the number of systems grows, so can the hardware footprint, power requirements, cabling, and maintenance effort.
What Is Real-Time Virtualization?
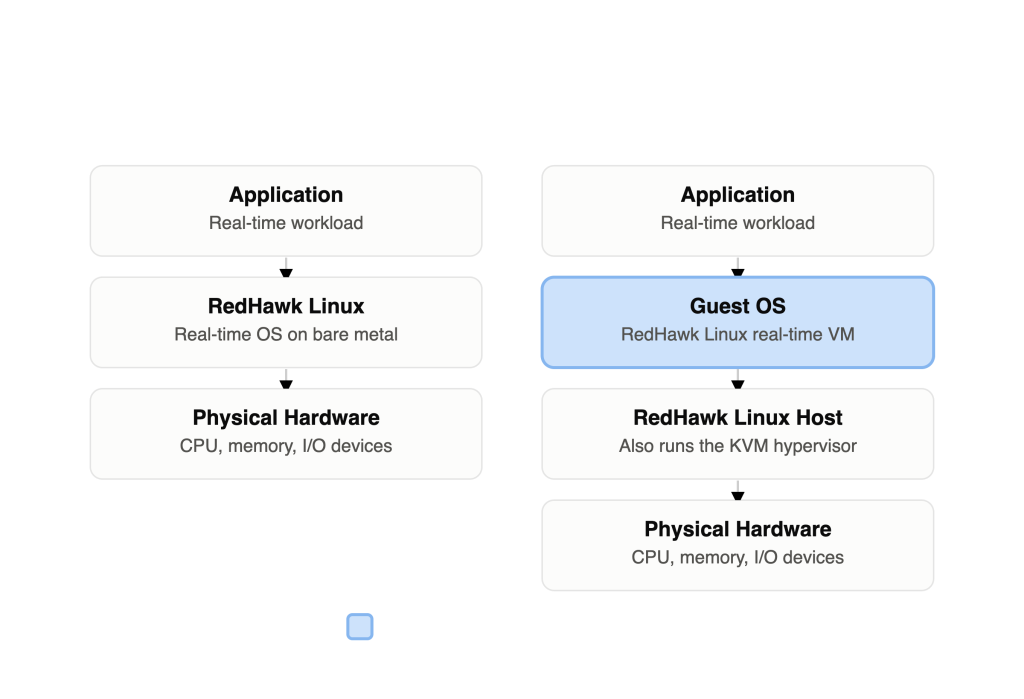
Real-time virtualization allows multiple operating-system environments to run on the same physical host. Each virtual machine can contain its own operating system, applications, libraries, drivers, and configuration.
This makes it possible to place timing-sensitive and general-purpose workloads on shared hardware while maintaining defined boundaries between them. It can also help preserve an existing software environment when the original hardware is no longer available or practical to maintain.
Real-time virtualization differs from conventional server virtualization in an important respect: resource allocation cannot be based only on average utilization.
A real-time virtual machine may need dedicated processor cores, local memory, controlled interrupt routing, and direct access to selected devices. Other virtual machines and host services must be prevented from interfering with those resources.
Virtualization therefore does not eliminate the need for system-level engineering. It changes where that engineering takes place.
When Native Real-Time Linux Is the Better Fit
A native architecture is generally the stronger choice when timing performance takes priority over consolidation or operating-system flexibility.
This may include applications such as closed-loop control, high-speed data acquisition, simulation, hardware-in-the-loop testing, and other workloads in which small timing variations can affect system behavior or test results.
Native deployment should be considered when:
- The application requires the lowest attainable latency and jitter.
- The system contains one primary timing-critical workload.
- Direct and predictable access to hardware is essential.
- The application uses specialized drivers or devices that are difficult to virtualize.
- The additional isolation provided by separate virtual machines is unnecessary.
- The team wants to minimize architectural complexity.
- System qualification already assumes a native operating environment.
Removing the virtualization layer does not automatically make a system deterministic. Processor sharing, interrupt activity, memory behavior, device drivers, and background services still need to be controlled. Native deployment simply gives the operating system more direct control over these factors.
When Real-Time Virtualization Is the Better Fit
Real-time virtualization becomes more useful when the system must support multiple workloads, operating systems, or software generations on a common hardware platform.
For example, a test system might include a real-time simulation, an operator interface, data logging, analysis tools, and an older application that depends on a previous operating-system release. Running each function on separate hardware may work, but it can create a larger and more difficult system to sustain.
A virtualized architecture may be appropriate when:
- Several existing computers can potentially be consolidated.
- Timing-critical and non-real-time workloads must run on the same host.
- Applications require different operating-system versions.
- An older validated environment must be preserved.
- Workloads need stronger separation from one another.
- Development teams need repeatable virtual-machine configurations.
- Hardware replacement would otherwise require substantial application changes or requalification.
- The system must support separate development, test, and production environments.
The primary advantage is not virtualization by itself. It is the ability to control the software environment independently from the physical system while deliberately assigning the hardware resources each workload needs.
Resource Isolation Is Central to the Decision
A virtual machine does not have exclusive control of the host simply because it has been assigned a certain number of virtual CPUs.
The physical processor cores supporting a timing-sensitive virtual machine must be considered alongside memory location, cache use, interrupt routing, I/O devices, and host activity. If another workload can compete for the same resources, it can affect response consistency.
A real-time virtualized design typically pins timing-critical work to dedicated, non-overlapping physical cores; shields those cores from host and other-VM activity; keeps processor, memory, and interrupt placement within the same NUMA node; and limits which host services can run alongside it.
These decisions depend on the physical topology of the server. A configuration that appears balanced at the virtual-machine level may perform differently if processors, memory, and devices cross NUMA boundaries.
Native systems benefit from the same attention to topology and resource placement, but the virtualized system adds another layer that must be configured and observed.
For a full breakdown of dedicated cores, NUMA-aware placement, and interrupt affinity, see How CPU Shielding, NUMA, and Interrupt Affinity Affect Real-Time Virtual Machines.
I/O Can Determine Whether Virtualization Is Practical
Processor scheduling receives much of the attention in discussions of real-time virtualization, but I/O is often just as important.
Virtual machines can access devices through emulation, virtualized drivers, PCI passthrough, or technologies such as SR-IOV. Each approach offers a different balance of compatibility, performance, sharing, and isolation.
Emulated devices are flexible, but they introduce additional software processing. Paravirtualized devices can reduce that overhead, although the host still participates in the I/O path. PCI passthrough gives a virtual machine more direct control of a physical device, but that device is normally unavailable to other virtual machines.
Before selecting virtualization, engineering teams should confirm:
- Which devices the application must access
- Whether those devices support passthrough or another suitable method
- Whether the required drivers are available in the guest operating system
- Whether devices need to be shared among workloads
- How interrupts will be assigned and routed
- Whether storage and network activity can interfere with timing-sensitive work
In some systems, the I/O requirements may point clearly toward native deployment. In others, careful device assignment can make consolidation practical.
Legacy Application Sustainment
Virtualization can be particularly useful for applications with long operational lifecycles.
An older application may depend on a specific operating-system release, library, compiler, or driver. Rebuilding it for a newer environment may introduce technical risk and require additional validation. At the same time, maintaining the original physical hardware becomes increasingly difficult as components become unavailable.
Placing the existing software environment in a virtual machine can separate its lifecycle from the lifecycle of the host hardware. The virtual machine can retain the expected operating system and application configuration while the underlying platform is replaced.
This approach does not remove every compatibility concern. Hardware-dependent drivers, licensing systems, and specialized devices still require evaluation. However, it can reduce the amount of the application stack that must change at one time.
System Visibility and Troubleshooting
Virtualization changes how timing problems must be investigated.
In a native system, engineers can examine application activity, operating-system scheduling, interrupts, system calls, memory use, and device behavior within one operating environment. In a virtualized system, an observed delay may originate in the guest, the host, the hypervisor, or a shared hardware resource.
Guest-only monitoring may therefore provide an incomplete explanation.
Engineers evaluating a virtualized architecture should consider whether their tools can help them:
- Examine host and guest activity
- Correlate events across operating environments
- Identify scheduling interruptions and context switches
- Review CPU and interrupt assignments
- Evaluate memory and NUMA placement
- Distinguish application delays from virtualization or I/O delays
The ability to observe the full system is important during initial configuration and remains important when applications, hardware, or workloads change.
A Practical Decision Framework
The decision between native and virtualized deployment should begin with application requirements rather than a preference for one architecture.
Start by asking:
- What is the application’s timing requirement, and how will it be measured?
- Is minimizing latency the overriding priority?
- How many operating environments must the system support?
- Are any applications tied to older software releases?
- Which physical devices must each workload access?
- Can processor, memory, interrupts, and devices be isolated appropriately?
- Does consolidation provide a meaningful operational or lifecycle benefit?
- Can the complete host-and-guest environment be monitored and validated?
- What changes would require the system to be tested or qualified again?
The answers may also support a mixed approach. The most timing-sensitive function can remain on a native system while supporting workloads are consolidated elsewhere. Virtualization does not need to include every application to provide value.
Choosing the Architecture
Native real-time Linux provides the most direct path between the application and the hardware. It is generally the preferred option when the lowest possible latency, direct device access, and minimal architectural complexity are the main requirements.
Real-time virtualization is better suited to systems that benefit from consolidation, workload isolation, legacy software preservation, or support for multiple operating environments. Those benefits come with additional configuration and validation requirements.
RedHawk Linux supports native real-time deployment, while RedHawk KVM-RT extends the environment to virtualized systems that require deliberate control of processor, memory, interrupt, and I/O resources.
Neither architecture is universally better. The correct choice is the one that satisfies the system’s measured timing requirements while keeping its hardware, software, and maintenance demands manageable over its intended lifecycle.
Learn more: Download our white paper, Real-Time Virtualization Without Compromising Determinism for a closer examination of the factors that affect timing behavior in a virtualized system.
Frequently Asked Questions
Can a virtual machine support a real-time application?
Yes, but running a real-time operating system inside a virtual machine is not sufficient by itself. The host must provide appropriate control over processor cores, memory placement, interrupts, and I/O resources, and the completed configuration must be tested against the application’s timing requirements.
Is native real-time Linux always faster than a virtualized deployment?
Native deployment removes the hypervisor layer and typically provides the most direct access to hardware. However, architecture decisions should be based on measured application requirements not speed alone. Virtualization may provide useful workload isolation, consolidation, and software-lifecycle benefits.
Can real-time and non-real-time workloads run on the same host?
They can, provided the timing-sensitive workload receives appropriately isolated resources. CPU assignments, memory locality, interrupt routing, I/O, and background host activity all need to be considered.
Does virtualization eliminate the need to update legacy applications?
No. It can preserve an older operating environment and reduce the number of components that must change at once, but hardware-dependent drivers, security requirements, licensing, and specialized I/O may still require updates or validation.
How should teams choose between native Linux and real-time virtualization?
Start with measurable timing, hardware-access, isolation, software-compatibility, and lifecycle requirements. Native deployment is generally stronger when the lowest practical latency and direct hardware access dominate. Virtualization becomes more useful when consolidation, multiple operating environments, or legacy sustainment provide meaningful benefits.
Related Articles
-

Preserving Legacy Real-Time Applications Through Virtualization
Preserving Legacy Real-Time Applications Through Virtualization Real-time applications often remain in service much longer than the hardware on which they were originally developed. Test systems, industrial controls, simulation environments, and data-acquisition platforms…
-

How CPU Shielding, NUMA, and Interrupt Affinity Affect Real-Time Virtual Machines
How CPU Shielding, NUMA, and Interrupt Affinity Affect Real-Time Virtual Machines Running a real-time operating system inside a virtual machine does not automatically create a deterministic environment. The virtual machine still depends…
-

Choosing an I/O Strategy for Real-Time Virtual Machines
Choosing an I/O Strategy for Real-Time Virtual Machines Processor allocation receives considerable attention when engineers design a real-time virtualized system. However, an application that interacts with physical equipment also depends on the…